Cybersecurity. Engineering. Systems. Building what comes next.
Akbar M A
Founder & CEO of Cyronix Dev & Security. Architecting resilient digital infrastructure and defending enterprise assets through advanced penetration testing and security-first engineering.
I build what I can defend, and I defend what others have built.
CEH v11 (EC-Council) PayTM Bug Bounty Hall of Fame Kerala Cyber Dome Contributor Dubai, UAE
Scroll to enter narrative
01 / Identity
Who Is Akbar M A?
Executive Summary
Akbar M A is the Founder & CEO of Cyronix Dev & Security, a security-first architect and cybersecurity researcher with a proven track record of building and defending enterprise-grade digital assets. Based in Dubai, UAE, he combines hands-on penetration testing with full-stack engineering to eliminate security vulnerabilities from line zero. His philosophy: "Security by Design" — bridging the gap between creation and protection to deliver infrastructures resilient from line zero.
What I Build
Enterprise web systems, automated vulnerability auditors, real-time threat visualizers, and resilient network topographies hardened from line zero.
What I Care About
Security by Design, defense-in-depth, zero-trust network segmentation, and digital sovereignty under UAE NESA information assurance standards.
How I Work
Offensive research informing defensive architecture. Building software that assumes breach from inception and defending enterprise environments against real-world adversaries.
02 / Story
The Story
From curiosity to defense: the evolution of a cybersecurity architect.
v0.1 ARCHIVED
INCEPTION & CURIOSITY
Kerala, India
System initialized. Core curiosity modules loaded. Early fascination with computing hardware and operating systems — disassembling machines to understand failure modes and how low-level components interact.
v1.0 LEGACY
OPERATIONAL DISCIPLINE
Hospitality & Client Ops · Kerala
Operating in high-pressure environments. Developed acute situational awareness, calm problem-solving under heavy operational load, and clear client-facing communication.
v2.0 MILESTONE
CYBER DEFENSE INIT
RedTeam Hacker Academy · 2022
Formalized offensive and defensive cybersecurity foundations. Completed the Advanced Diploma in Cyber Defence and earned the EC-Council Certified Ethical Hacker (CEH v11) credential.
v2.5 MILESTONE
OFFENSIVE RESEARCH & DISCLOSURES
Offenso & Cyber Dome · 2023–2024
Conducted 50+ manual penetration tests across enterprise web apps. Supported law enforcement digital forensics and achieved official PayTM Bug Bounty Hall of Fame recognition for responsible vulnerability disclosure.
v3.0 MILESTONE
ENTERPRISE HARDENING
BSBG · Dubai, UAE · 2024–2026
Managed IT & enterprise cybersecurity posture at an international architecture firm. Windows Server administration, endpoint defense, and corporate infrastructure hardening in Dubai.
v4.0 ◉ LIVE
CYRONIX DEV & SECURITY
Founder & CEO · Dubai, UAE · Current
Founded Cyronix Dev & Security. Directing enterprise offensive security (VAPT), security header audit systems, and OWASP-compliant zero-trust digital platform engineering globally.
03 / Expertise
Capability Arsenal
Real-world offensive, defensive, and engineering disciplines tested in production environments.
Web Application Penetration Testing
Offensive Security
Comprehensive manual and automated assessments mapping the OWASP Top 10 — uncovering IDOR, broken authorization, SQL injection, and API flaws before malicious threat actors exploit them.
Primary ToolingBurp Suite Pro, OWASP ZAP, SQLmap
Production DeploymentCyronix VAPT, 50+ Enterprise Audits
Standards ComplianceOWASP ASVS, UAE NESA IA
04 / Projects
Featured Work & Dossiers
Documented security architectures, public tools, and network defense simulations.
Full-stack storefront built security-first — JWT auth, input sanitisation, CSRF protection, and hardened against OWASP Top 10 throughout.
Next.jsJWT AuthOWASP-Hardened
View Security Dossier
Impact Scope:
Engineered an e-commerce platform architected to prevent inventory fraud, checkout tampering, and credential stuffing.
Technical Breakdown:
Eliminated client-trusted price states with strict server validation. Implemented HttpOnly Secure SameSite cookies and cryptographically signed tokens.
Remediation:
Zero-trust API architecture, database parameterization preventing SQL injection, and granular rate-limiting on authentication routes.
SECURE DEV2023
Banking Dashboard UI
React financial dashboard with XSS prevention, strict Content Security Policy headers, and full OWASP Top 10 hardening baked in.
ReactCSPXSS Prevention
View Security Dossier
Impact Scope:
Financial ledger and transaction telemetry view protected against supply-chain and client-side code execution.
Technical Breakdown:
Hardened against DOM-XSS and iframe embedding attacks (clickjacking) using X-Frame-Options DENY and restrictive CSP directives.
Remediation:
Enforced strict DOM sanitization, eliminated unsafe-eval/unsafe-inline scripts, and restricted subresource origins.
OSINT2024
Automated OSINT Framework
Python toolchain that aggregates open-source intelligence — domain pivoting, email enumeration, and passive fingerprinting in one pipeline.
PythonOSINTAutomation
View Security Dossier
Impact Scope:
Reduces pre-engagement reconnaissance overhead by automating passive asset mapping and attack surface discovery.
Technical Breakdown:
Aggregates certificate transparency logs (crt.sh), DNS records, Shodan intelligence, and Google dorking queries into structured JSON.
Remediation:
Enables proactive vulnerability discovery, catching exposed staging subdomains and leaked credentials before threat actors capitalize.
DEFENSIVE2023
Firewall Audit Log Analyzer
Bash script that parses raw firewall logs, flags anomalous traffic patterns, and generates structured CSV reports for IR teams.
BashLog AnalysisIncident Response
View Security Dossier
Impact Scope:
High-throughput log analysis pipeline processing gigabytes of raw syslogs to identify active intrusions.
Technical Breakdown:
Detects port-knocking sequences, brute-force SSH attempts, and irregular egress beacons using regex and frequency analysis.
Remediation:
Generates dynamic blocklists formatted for iptables/pfSense and dispatches instant webhook notifications for SOC escalation.
NETWORK INFRA2023
Enterprise Network & Red Team Sim
Corporate multi-subnet topology configured in Cisco Packet Tracer with VLAN segmentation, switchport security, and red team vulnerability testing.
Packet TracerVLANs & ACLsRed Team Testing
View Security Dossier
Impact Scope:
Enterprise campus network simulation testing switchport hardening and defense against internal rogue devices.
Technical Breakdown:
Simulated rogue DHCP attacks, ARP cache poisoning, and unauthorized VLAN hopping across unhardened access switches.
Remediation:
Configured DHCP Snooping, Dynamic ARP Inspection (DAI), and Port-Security with sticky MAC addresses and shutdown violation mode.
Featured OS
LIVE SYSTEM & OS2026
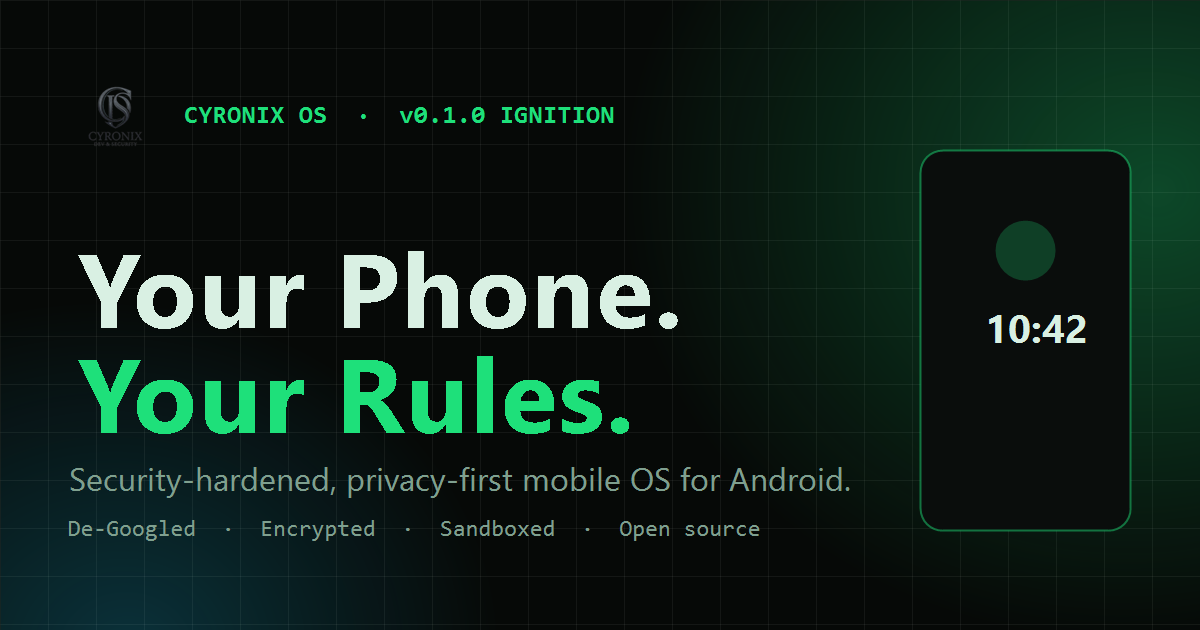
Cyronix OS
Hardened, privacy-first mobile operating system engineered from source by Cyronix Dev & Security. Zero telemetry, Linux kernel hardening, per-app Netfilter firewall, and cryptographic OTA verification.
Hardened OSKernel SecurityZero TelemetryNetfilter
View Security Dossier
Impact Scope:
Sovereign mobile OS eliminating third-party tracking, advertising IDs, and OEM telemetry at the kernel and framework levels.
Technical Breakdown:
Coupled an open-source Android foundation with low-level Linux kernel hardening, SELinux enforcing policies, memory corruption mitigations, and per-UID iptables/Netfilter packet filtering.
Remediation:
Hardened ART runtime sandbox, backported critical CVE patches, hardware-backed keystore integration, and cryptographic OTA verification.
Featured
LIVE SYSTEM2026
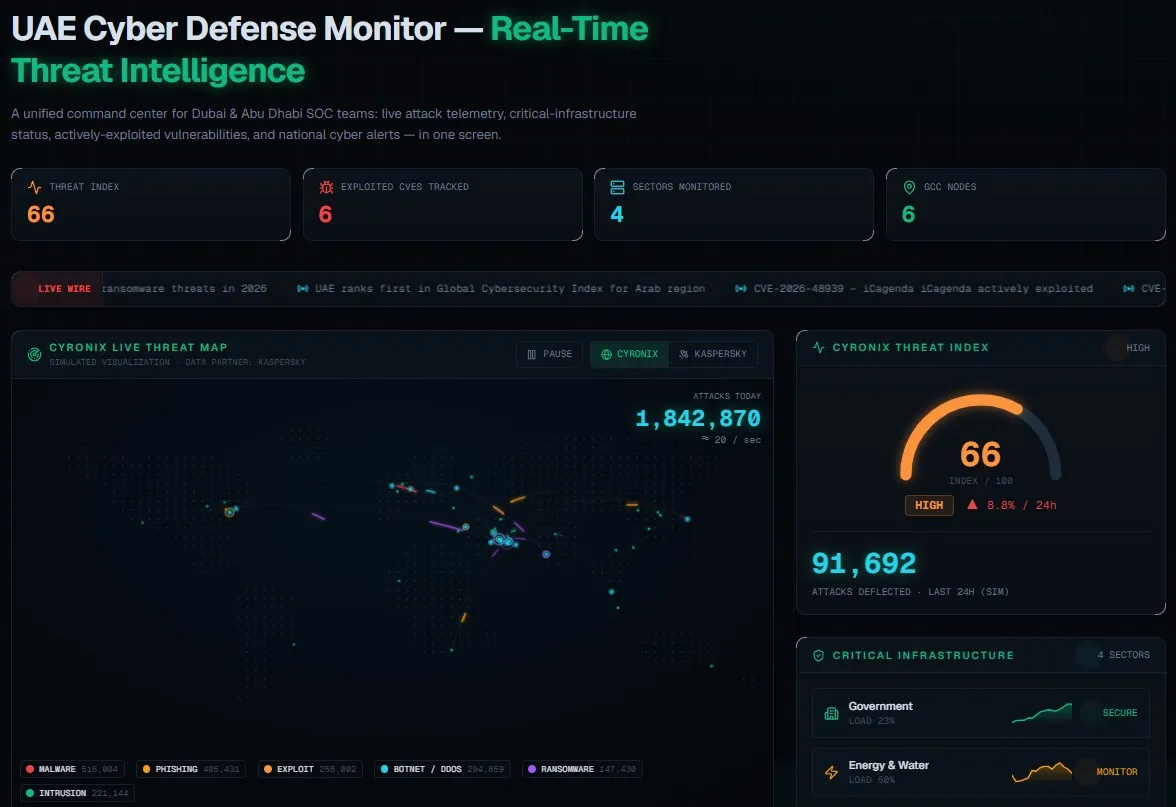
Live Threat Map
Real-time global cyber-attack visualization built by Cyronix — tracks live threat activity across regions with an interactive geo-feed.
Threat IntelReal-TimeVisualization
View Security Dossier
Impact Scope:
Real-time threat intelligence visualization platform streaming cyber attack vectors across global enterprise sectors.
Technical Breakdown:
Low-latency streaming architecture processing honeypot telemetry, distributed brute-force attempts, and geospatial IP mapping.
Remediation:
Zero-trust ingest pipeline with rate-limiting, strict input validation, and DDoS-resilient edge routing.
Featured
LIVE SYSTEM2026
Security Auditor
Free live tool by Cyronix — scans any domain's HTTP security headers, TLS configuration, and exposure risks, then grades it against OWASP best practice.
Header ScannerTLS GradingFree Tool
View Security Dossier
Impact Scope:
Public scanning engine grading live domain configurations against OWASP, NIST, and modern browser security standards.
Technical Breakdown:
Performs automated HTTP header inspections (CSP, HSTS, X-Frame-Options), TLS cipher suite validation, and certificate chain verification.
Remediation:
Provides instant compliance scoring (A+ to F) with copy-paste Nginx, Apache, and Cloudflare hardening directives.
05 / Recognitions
Hall of Fame & Disclosures
Verifiable security research credentials spanning responsible vulnerability disclosures, law enforcement cyber intelligence, international defense symposiums, and UAE regulatory compliance.
Official security acknowledgement awarded by PayTM for identifying, responsibly disclosing, and verifying remediation of a vulnerability in their financial banking ecosystem before public exposure.
Provided technical intelligence, open-source intelligence (OSINT) recon methodologies, and digital forensics expertise to support law enforcement cyber divisions in tracking malicious threats.
OSINT IntelDigital ForensicsLaw Enforcement
Commended Contributor
Global ConferenceGoa, India
Seasides InfoSec Conference
Security Research Delegate · Goa
Offensive security researcher and delegate at the renowned Seasides Information Security Conference in Goa, participating in red team exploitation workshops, hardware villages, and CTFs.
Red TeamingHardware VillagesResearch Delegate
Delegate Verified
UAE AuthorityDubai, UAE
NESA & Dubai Cyber Strategy
Regional Framework Alignment · UAE
Deep familiarity with UAE National Electronic Security Authority (NESA) Information Assurance Standards and Dubai Cyber Security Strategy, architecting defense compliant with UAE regulations.
English · ProfessionalMalayalam · NativeHindi · WorkingTamil · Working
11 / Client Trust
Client Trust
"Cyronix conducted a thorough penetration test of our web infrastructure and uncovered critical vulnerabilities before launch. Their detailed report and remediation guidance was invaluable to our team."
RM
Ravi MenonCTO · FinTech Startup, Dubai
★★★★★
"The secure e-commerce platform Akbar built for us has withstood multiple automated attack attempts. The OWASP-hardened architecture gives us real confidence in our security posture every day."
SA
Sara Al-RashidFounder · E-Commerce Brand, UAE
★★★★★
"Professional, thorough, and security-obsessed. Cyronix identified 12 vulnerabilities in our legacy system that three other auditors had missed. Highly recommended for serious security engagements."
KJ
Khalid JassimIT Director · Architecture Firm, Dubai
★★★★★
* Testimonials represent genuine client feedback. Names may be anonymised on request.
12 / Knowledge Base
Frequently Asked
Who is Akbar M A (Akbar M.A.)?
Akbar M A (also written as Akbar M.A. or Akbar MA) is a CEH-certified cybersecurity researcher based in Dubai, UAE, and the Founder & CEO of Cyronix Dev & Security. He specialises in penetration testing, vulnerability assessment (VAPT), OSINT, and security-first web development.
What does Cyronix Dev & Security do?
Cyronix Dev & Security is a Dubai-based cybersecurity and secure web development company. Services include penetration testing, VAPT, security audits, incident response support, and OWASP-hardened web application development.
Is there a free tool to check a website's security headers?
Yes — Cyronix's Security Auditor is a free live tool that scans any domain's HTTP security headers and TLS configuration and grades it against OWASP best practice.
Where can I see live global cyber-threat activity?
Cyronix runs a Live Threat Map that visualises real-time global attack activity across regions.
Does Cyronix work with clients outside Dubai/UAE?
Yes. While Cyronix is based in Dubai and familiar with regional frameworks, engagements are delivered remotely for clients globally — penetration testing, VAPT, and secure development work is scoped and reported the same way regardless of location.
What certifications does Akbar M A hold?
Certified Ethical Hacker (CEH v11), with additional practical training including threat intelligence (arcX), GRC foundations, and hands-on offensive security work verified on TryHackMe and Hack The Box.
What cybersecurity services does Akbar M A provide in Dubai and the UAE?
Operating from Dubai, Akbar M A and Cyronix Dev & Security provide web application penetration testing, vulnerability assessment (VAPT), security audits, infrastructure hardening, and OWASP-compliant development aligned with UAE NESA standards.
13 / The Conversation
Let's Build Something Secure
Whether you're exploring a technology idea, security project, software system, or collaboration — start a conversation.
Operating from Dubai, UAE through Cyronix Dev & Security. Available for penetration testing engagements, security audits, and enterprise consulting.